Overview
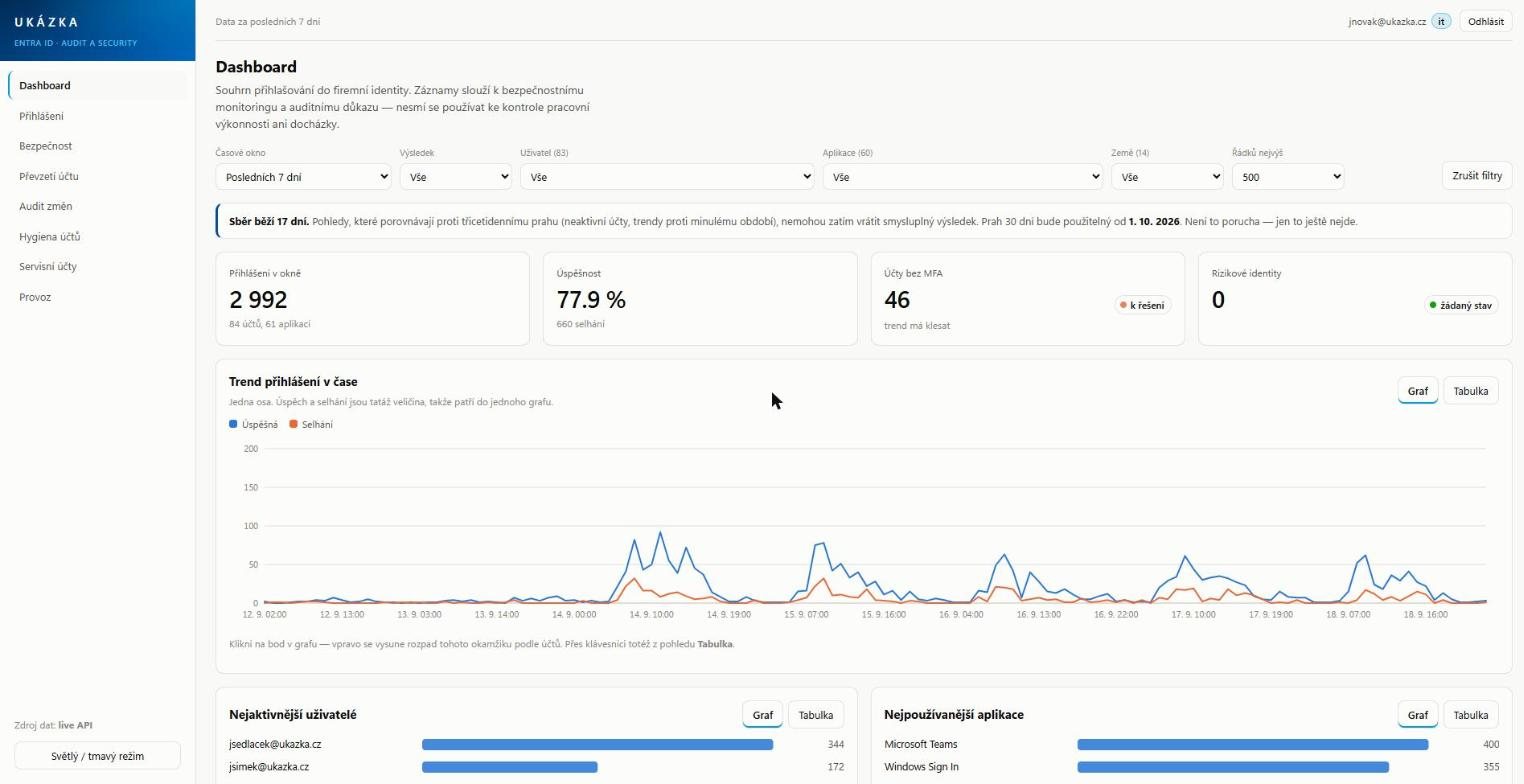
how many sign-ins, what success rate, how many accounts without MFA.
Case study
An app over logs from Microsoft Entra ID.
Entra ID keeps logs only for a limited time, and when an auditor asks what happened half a year ago, the portal has no answer. Logs are therefore collected into Log Analytics with its own retention, with an app on top where you can search without writing KQL queries.
eight sections, each answering a different question:
how many sign-ins, what success rate, how many accounts without MFA.
detail of interactive sign-ins by filter.
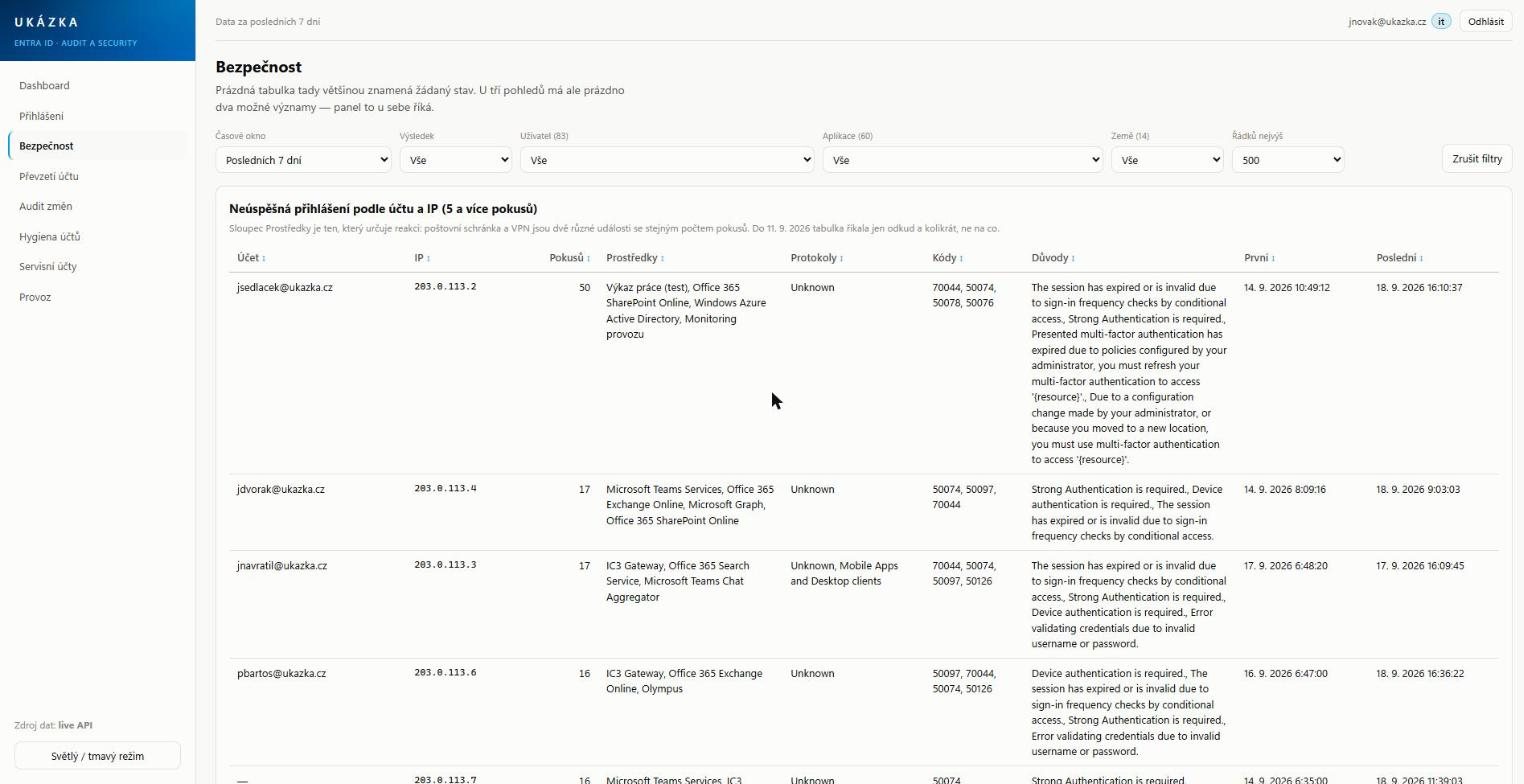
repeated failed sign-ins by account and IP.
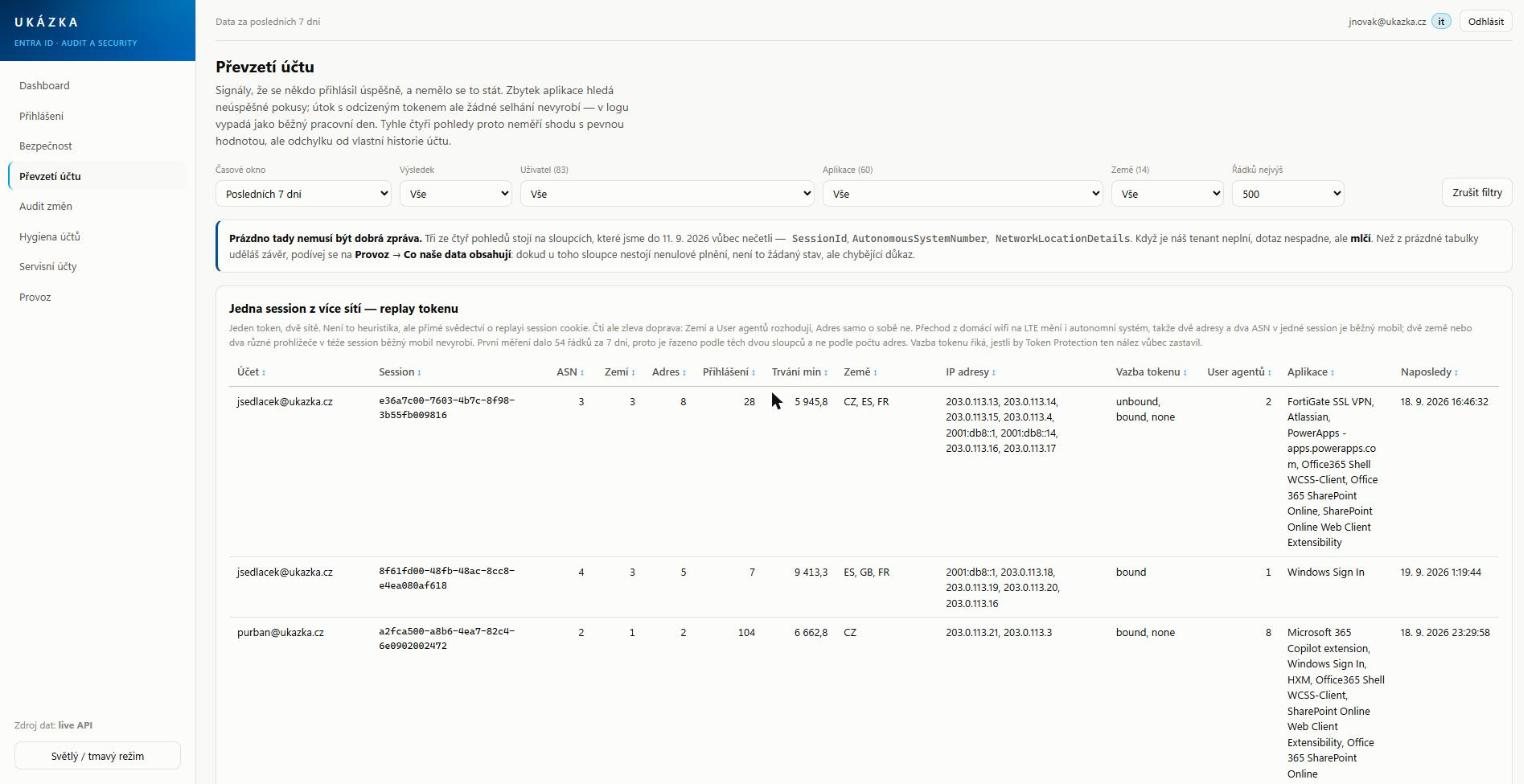
signals that someone signed in successfully when they shouldn't have.
who changed permissions, roles and settings.
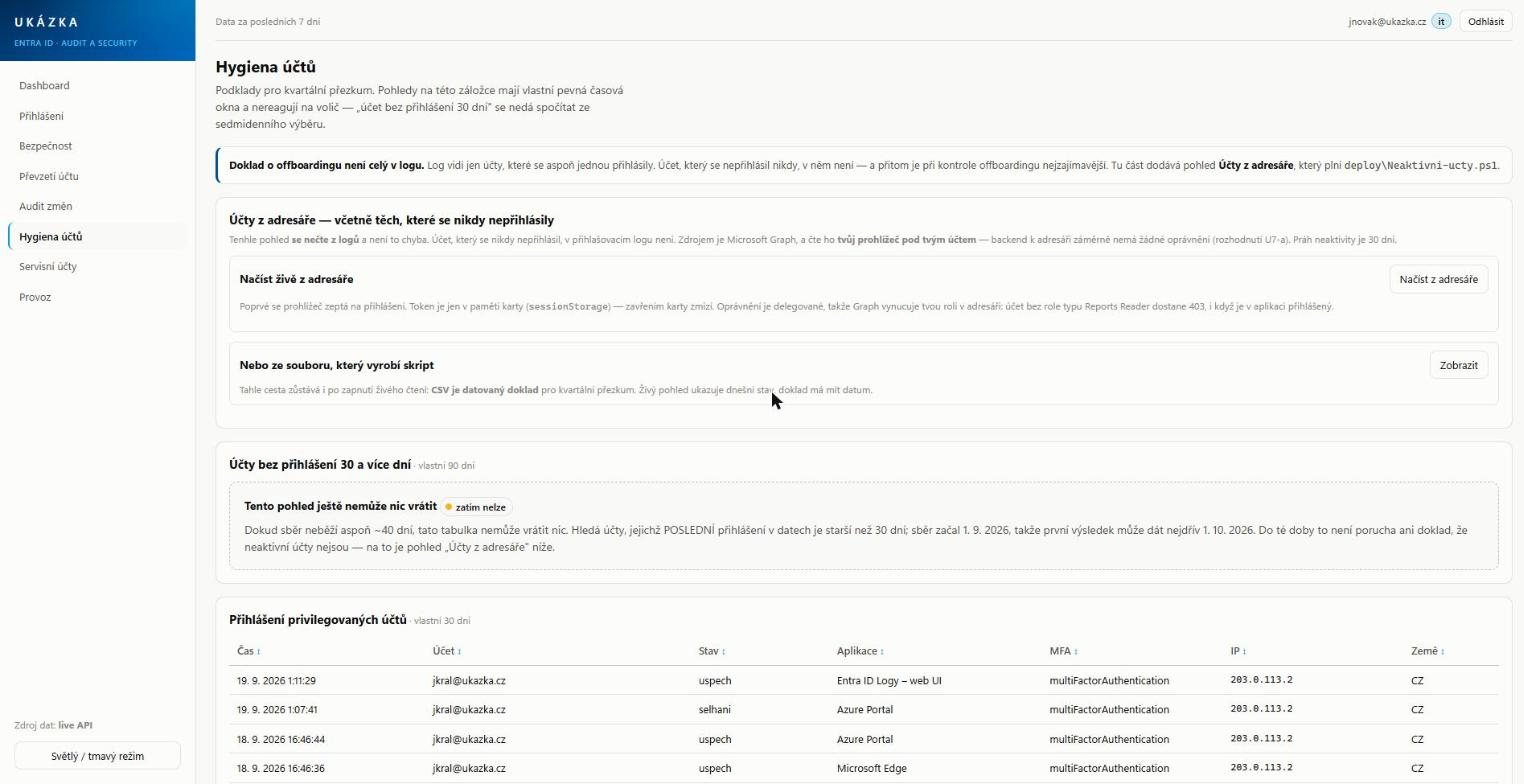
a basis for quarterly reviews — inactive accounts, privileged accounts.
applications and service principals that reviews tend to forget.
collection health, data volume and cost estimate.
For every view the app says whether empty means the desired state or missing evidence. Until collection has run long enough, views computed against a thirty-day threshold openly report that they can't return anything yet — instead of returning an empty table that looks like good news.
An attacker with a stolen token produces no failure; in the log they look like an ordinary workday. Views in this section therefore don't measure conformance to a fixed value but deviation from the account's own history — for example one session signing in from several networks and countries at once.
Anyone not in it gets an explanation instead of data — that it's about permissions, not an error — and an instruction to write to IT; nobody adds themselves.
The app states it in the first place a user looks: records serve security monitoring and audit evidence, not checking people's work performance or attendance.
an audit trail for ISO/IEC 27001 and ISO 9001, a basis for quarterly access reviews, and the answer to “who, when, from where and with what” before anyone asks.
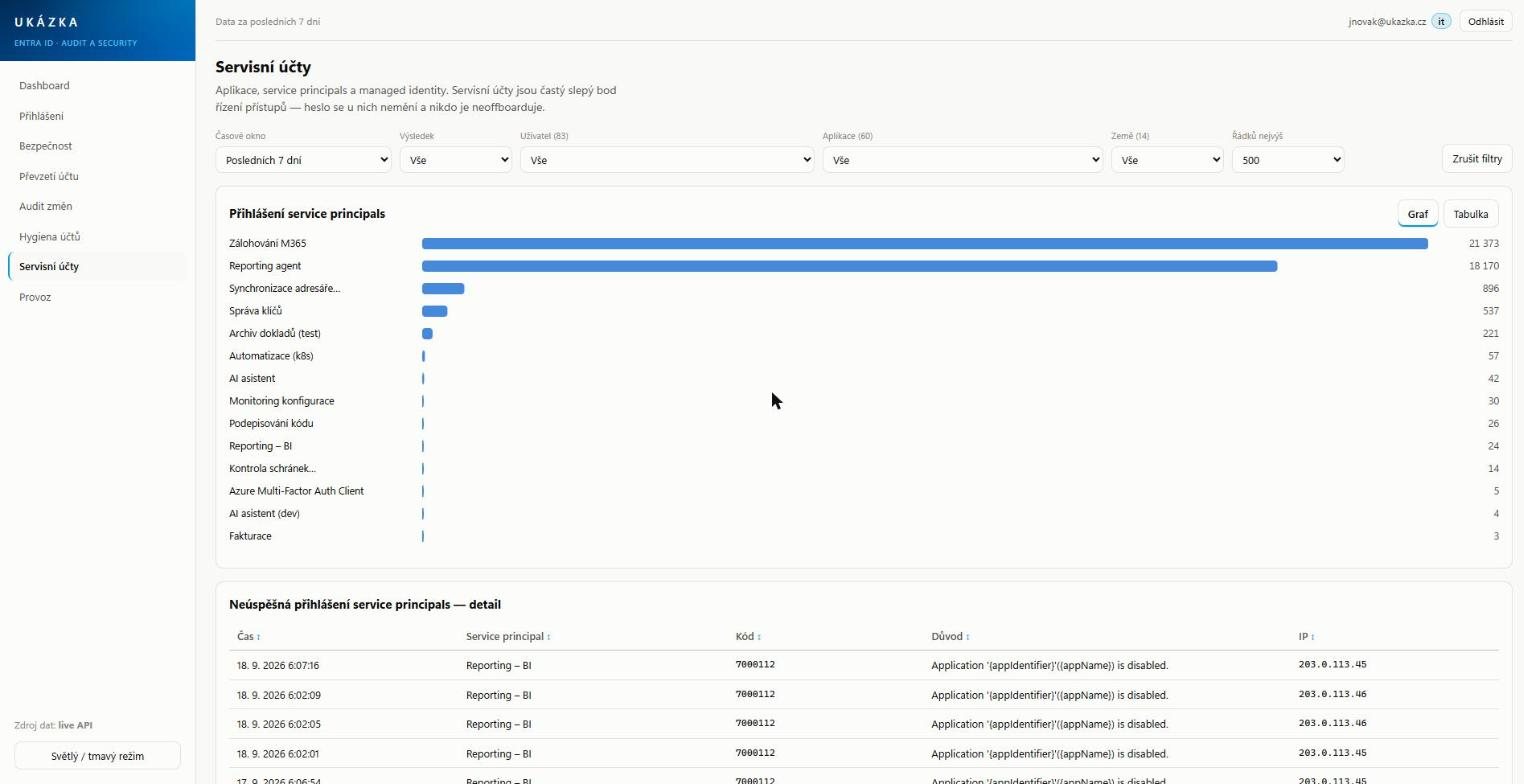
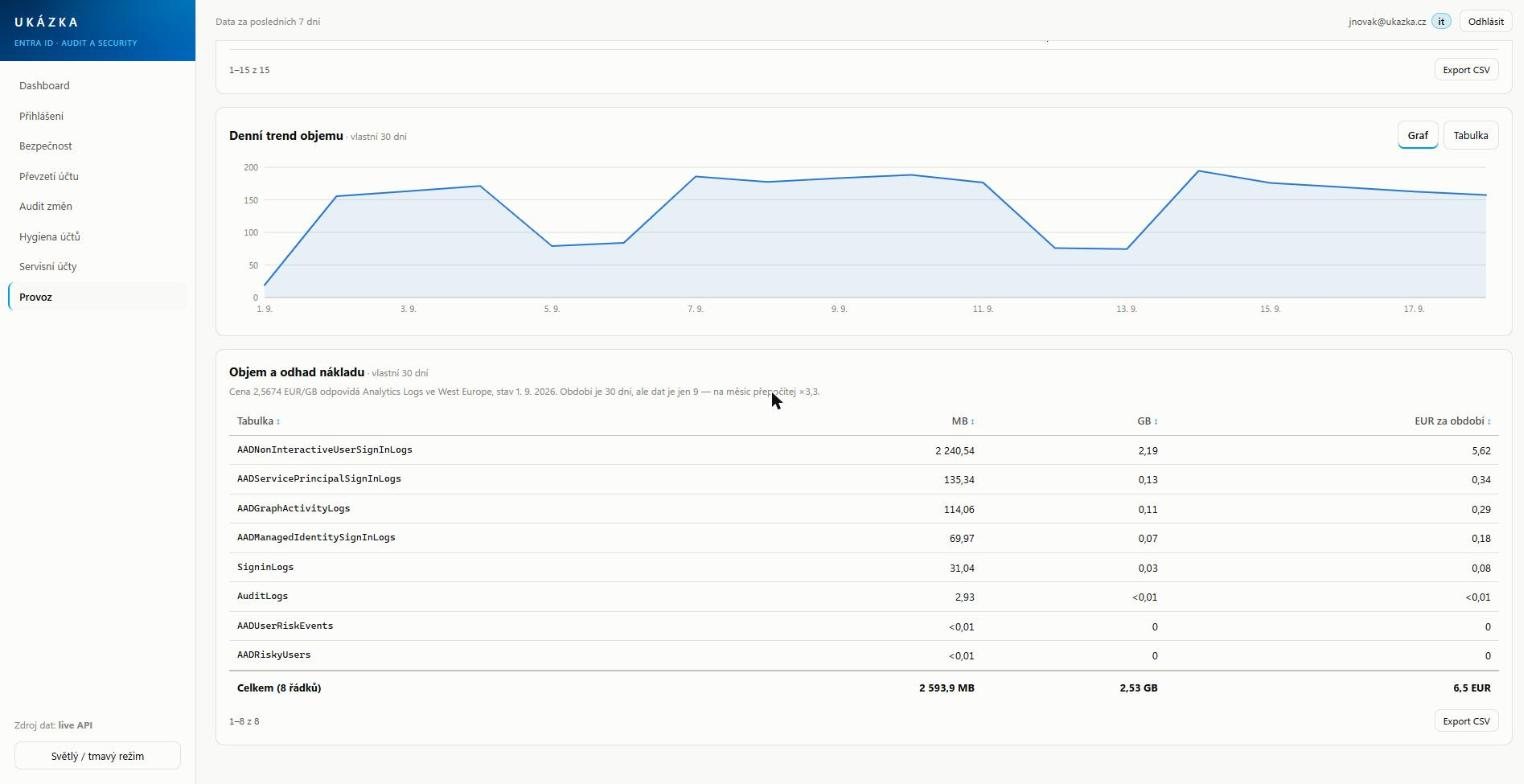
Tap a snapshot to enlarge it. The data in the snapshots is anonymized.
Microsoft, Azure, Microsoft 365, Entra, Teams, SharePoint, Intune, Defender and Copilot are trademarks of the Microsoft group of companies.
NOVOTNACI is an independent service provider and is not owned by or affiliated with Microsoft. · © 2026 NOVOTNACI ·
Privacy Policy ·
This site uses no cookies and no analytics.